New PHP2Shell scanner checks your hosts for CVE-2026-109618 and CVE-2026-109619
Searchlight Cyber released php2shell-scanner, an open-source tool that tests whether a host is exposed to CVE-2026-109618 and CVE-2026-109619, the pair of PHP remote code …
Info-stealing malware slipped into OVHcloud CLI releases on GitHub
OVHcloud, the French cloud computing and web hosting company, alerted customers that a hacker tampered with its open-source command-line interface (CLI) tool to spread …
DevGuard: Open-source vulnerability management for the software supply chain
DevGuard is a free, open source vulnerability management platform that collects a software project’s security findings in one place, ranks them by risk, and tracks them. …
Google open-sourced TorchTPU, so PyTorch on TPUs just got a lot easier
Google released TorchTPU as open source, giving PyTorch developers a native way to run models on the company’s Tensor Processing Units. Google also announced TPU support in …
Bearer CLI: Free, source-available code security scanning tool (SAST)
Bearer CLI is a free static application security testing (SAST) tool that scans source code for vulnerabilities and prioritizes them by the sensitive data they touch. SAST …

GitHub adopts cheaper AI model to catch secrets developers leave in code
GitHub has trained a credential classifier to improve generic secret detection and reduce false alerts. The new pipeline cut median post-push scan execution time by 86% and …
Meshery: Open-source cloud-native manager for Kubernetes
Meshery is an open-source tool for designing, deploying and managing Kubernetes infrastructure, built by Layer5 and its community and hosted as a Cloud Native Computing …
npm Trusted Publishing flaw exposed 1,500+ npm packages to takeover
Bloom Security researchers found that npm’s Trusted Publishing feature let an attacker push new versions of someone else’s package without stealing a credential. The attacker …
Strands Box: Open-source sandbox for AI agents
AWS released Strands Box, an open source sandbox for AI agents that pairs operating-system isolation with rules that can weigh what an agent has already done before letting it …
Cryptomining botnet hides C2 addresses in GitHub poem, infects over 3,400 servers
Thousands of hijacked servers have been looking up their command and control (C2) server in a poem posted on GitHub, according to Black Lotus Labs. The malware reading it, …
GitHub adds AI to catch passwords before a code push
GitHub has announced an AI detector, developed with Microsoft Applied Sciences, to help prevent developers from uploading passwords and other credentials to code repositories. …
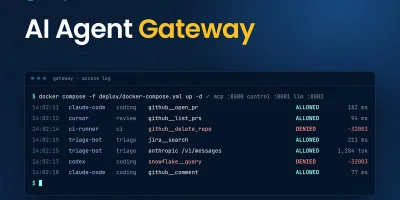
AI Agent Gateway: Open-source tool keeps credentials out of agent configs
Tuskira’s AI Agent Gateway is an open-source solution that sits between AI agents and everything they call: the MCP tool servers that connect them to services like …
Featured news
Resources
Don't miss
- Hackers hijack exposed AI models to launch cyberattacks at victims’ expense
- Drone program compliance: What a CTO says most agencies get wrong
- LiteLLM hit by second supply chain attack this year, users urged to rotate credentials
- OpenAI’s coding agents talked themselves out of being monitored
- New PHP2Shell scanner checks your hosts for CVE-2026-109618 and CVE-2026-109619