
AI uncovers flaws in discontinued devices with no vendor left to patch them
Forescout researchers built a tool to test if generally available AI models could find security flaws on a limited budget. They examined both open-source code and compiled software whose source code was unavailable, testing an approach attackers could also use.
The team confirmed 99 vulnerabilities across 10 TCP/IP stacks, the software components that allow devices to communicate over networks. Sixty-six were previously unknown, and 52% of those newly discovered vulnerabilities were rated as high or critical in severity.
The affected software is used in industrial equipment, medical devices, network equipment and other connected products. Siemens has identified affected building automation controllers in its APOGEE, Desigo and TALON product lines, while other vendors continue to investigate.
“Our research demonstrates that AI is changing the economics of vulnerability discovery and accelerating the pace at which security teams need to identify, prioritize, and mitigate cyber risk. This is especially impactful for critical infrastructure, where legacy and difficult-to-patch devices may remain in service for years,” said Daniel dos Santos, VP of Research at Forescout.
Researchers taught the system what to look for
The team built its system around Claude models and existing security tools, drawing on years of research into embedded software.
Code scanners first flagged patterns that could indicate a vulnerability. AI agents then examined if an attacker could reach the suspect code and exploit the potential weakness. In the final stage, the system attempted to run the software and produce a test that triggered the issue, with researchers able to intervene and guide the work.
Records from earlier investigations helped the researchers create 32 scanning rules. These covered problems such as copying more data than a memory buffer can hold or mishandling information received over a network. The team reviewed and refined the rules before using them.
The 90-hour comparison includes validation
Automated analysis took about 10 hours, followed by approximately 80 hours of validation. The researchers compared this with roughly nine months of manual code analysis during Project Memoria, an earlier investigation conducted in 2020 and 2021.
Project Memoria lasted 18 months overall and covered 14 networking stacks over several phases. This study examined 10 stacks, including seven that had been studied before.
The time and cost estimates cover applying the completed system to those targets. Building the system required additional work to develop scanning rules, prepare environments for running the software and refine the instructions given to AI agents.
Automated code inspection cost $935. Including estimated spending on tests that ran the software, total model costs ranged from approximately $1,200 to $2,300.
Testing ruled out many suspected flaws
The automated process produced 362 initial findings, leaving 312 candidates after duplicates were removed. Testing and review confirmed 99 vulnerabilities.
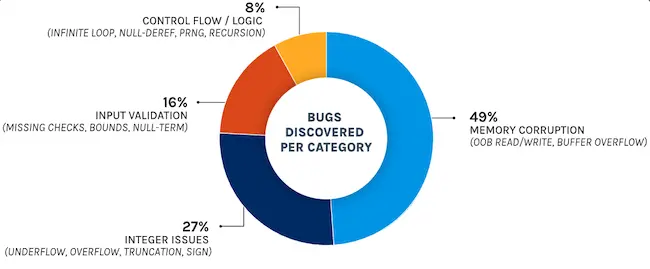
The 99 vulnerabilities discovered by the harness, grouped by category (Source: Forescout)
The system rediscovered 33 of the 82 known vulnerabilities used for comparison. It performed best at finding memory errors in code that processes network traffic. Problems involving software logic or design, such as predictable values intended to be random, were harder to detect.
Compiled software required more work. Without source code, the tools had to reconstruct a usable representation of the program, a process that can introduce inaccuracies and generate false alarms. Automated inspection of these targets cost about six times as much and took roughly twice as long as source-code inspection.
Some vulnerable products have no vendor left to fix them
The team reported 54 of the newly discovered vulnerabilities to developers and maintainers because it believed they still affected the latest versions. Several projects have issued fixes. Investigations remain open for three networking stacks whose names have been withheld during the disclosure process.
One investigation involved firmware from a discontinued wireless access point made by a company that had ceased operating. During that analysis, the system also found seven device-specific vulnerabilities, including administrator credentials that could not be changed and a buffer overflow in the firmware upload process.
“Organizations still have legacy systems, operational requirements, and devices that can’t easily be patched or simply taken offline. Containing risk, rather than patching, must be the priority,” said Barry Mainz, CEO at Forescout.
Such products can remain in use after their manufacturer has ceased operating, leaving no supplier available to develop or distribute a patch.
